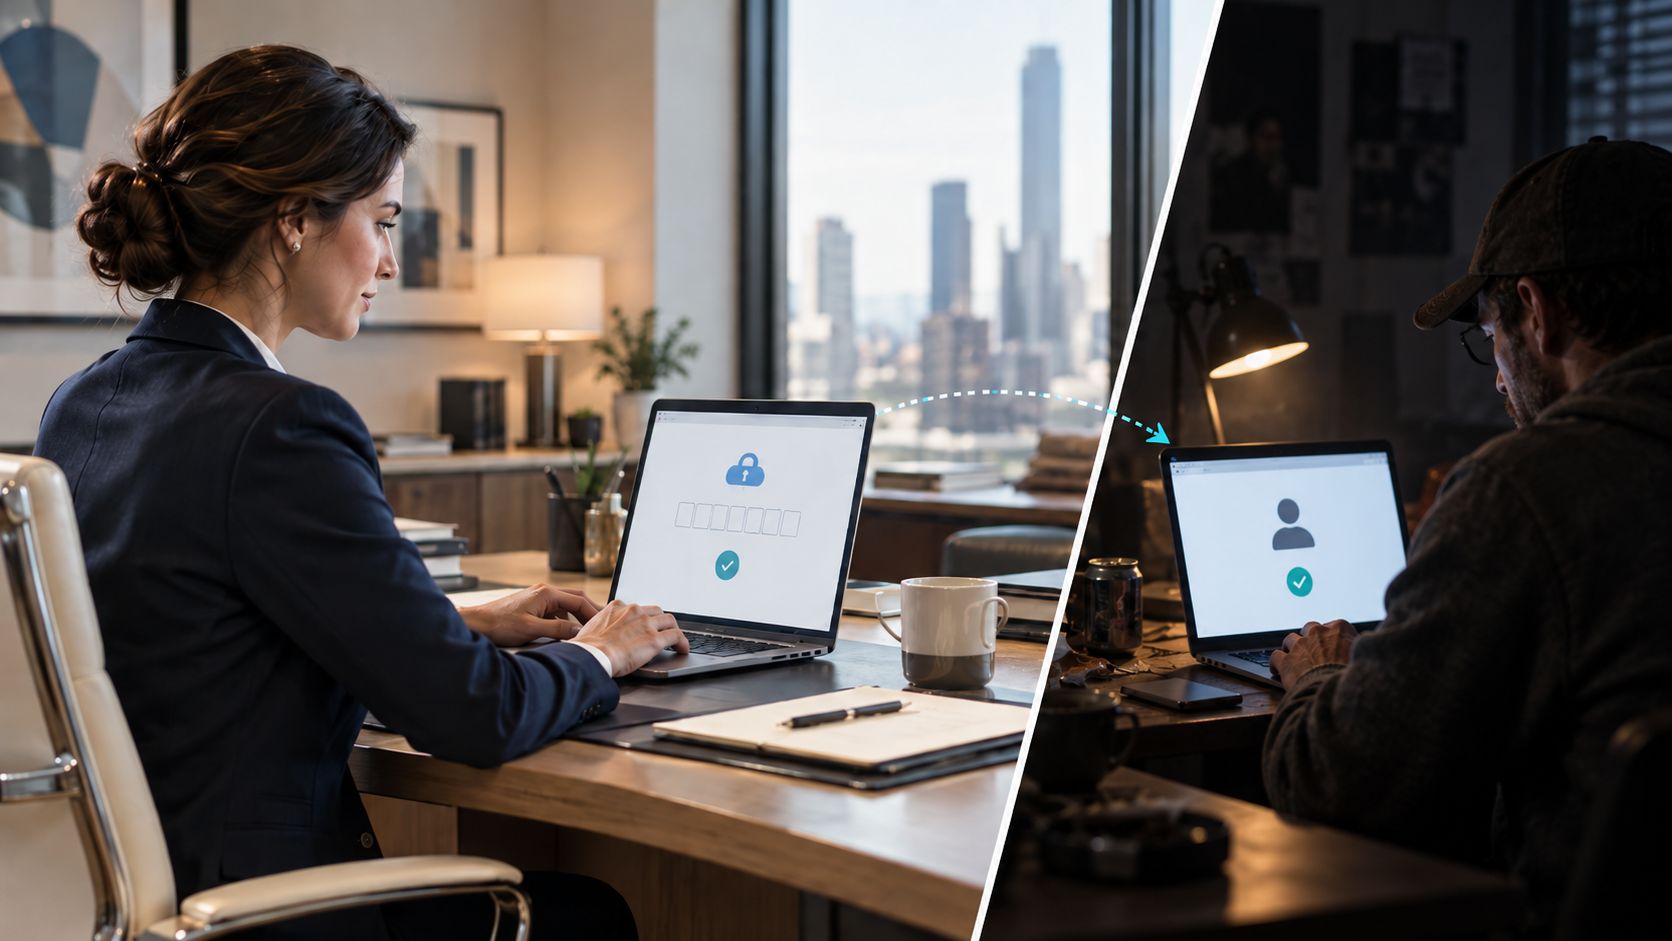
By the middle of a normal workday, an attorney or staff member may have opened a document shared by a client, reviewed an electronic signature request, followed a link from co-counsel and signed back into Microsoft 365 after a session expired.
None of that is unusual. Signing in has become part of legal work.
That familiarity is exactly what makes a newer phishing technique, device code phishing, so effective.
First, a quick definition. A device code is a short string of letters and numbers, usually eight or nine characters, that a device displays when it cannot easily handle a normal sign-in screen. You type that code into a Microsoft page on your phone or laptop, sign in there, and the device is granted access. It is a normal Microsoft feature, not a trick.
Two more words are worth separating, because the rest of this article turns on the difference. Authentication is proving who you are, such as entering a password and approving a multifactor prompt. Authorization is what happens next: deciding what that proven identity is allowed to reach, and handing over the access. Most security training focuses on the first. Device code phishing attacks the second.
Device code phishing does not necessarily rely on convincing someone to enter a password on a fake Microsoft page. Instead, an attacker can manipulate a legitimate authentication process so the user unknowingly authorizes a session the attacker controls.
The technique has gained significant attention in 2026. Microsoft documented a widespread campaign abusing this device code sign-in method, while the FBI issued a separate warning about the Kali365 phishing-as-a-service platform.
For law firms, the mechanics are important. But the larger identity risk is even more relevant: attackers are learning how to make malicious authorization look like one more routine step in getting work done.
Device code phishing abuses authorization, not just passwords
Device code authentication has legitimate uses. It was designed for devices that are difficult to sign into directly, such as smart TVs or printers. The device displays a short code, which the user enters in a browser on another device to complete authentication.
Device code phishing turns that process around:
- The attacker initiates the authorization request and receives a valid device code.
- The user receives a believable lure, such as a document review or other business request.
- The user enters the supplied code through the legitimate authentication process and may complete multifactor authentication (MFA).
- The attacker receives authorized access because the session being approved belongs to the attacker, not the employee.
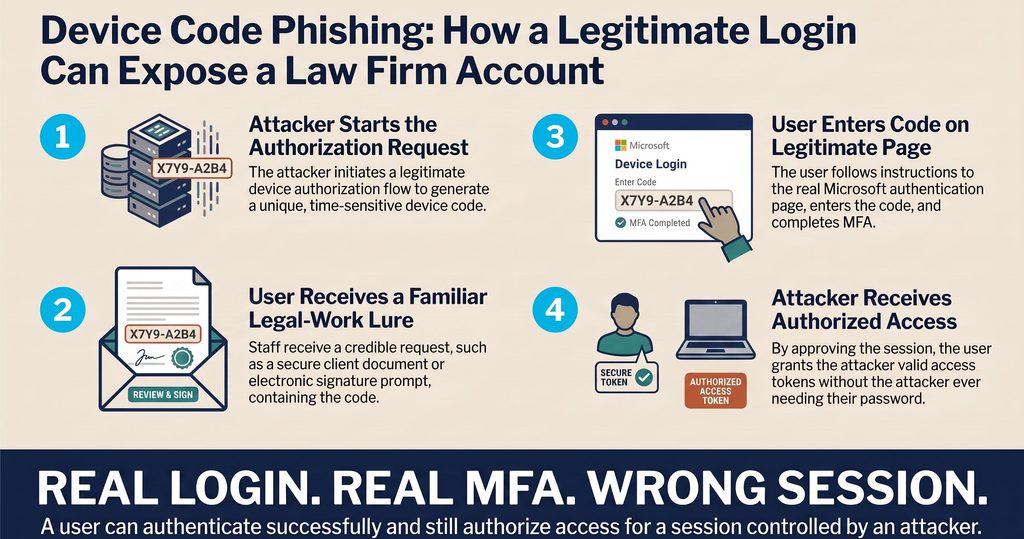
That last step is what makes the technique so counterintuitive. The user may never type a password into a fake login page. In campaigns documented by Microsoft, victims were ultimately sent to the legitimate Microsoft device login portal. Once the user completed the process, the attacker walked away with valid digital keys to the account, including the ability to stay signed in without ever being asked for the password again.
Legal workflows give the attack credibility
A phishing email telling an attorney to claim a lottery prize is probably not going very far. A request to review a document is another matter. Recent device code campaigns have been disguised as invoices, shared files, voicemail notifications and electronic signature requests. Mimecast reported observing more than 50,000 malicious device code phishing campaigns beginning in March 2026, including campaigns impersonating DocuSign and even security enrollment workflows.
Those lures fit naturally into legal work. Attorneys and staff routinely interact with:
- Client documents and secure file-sharing systems
- Electronic signature requests
- Files from co-counsel, experts and other outside parties
- Client and vendor portals
- Microsoft 365 notifications and authentication prompts
The problem is not that employees are ignoring obvious warning signs. Device code phishing can make the authentication step itself look trustworthy because part of it actually is. That changes the security-awareness conversation. Checking the domain and looking for a fake login page still matter, but they cannot be the only tests an employee uses to decide whether an authentication request is safe.
The employee authenticates, the attacker gets authorized
Device code phishing is often called an MFA-bypass attack, but that is not really what happens. Authentication works exactly as designed. Authorization is where it goes wrong. MFA has not suddenly become irrelevant. It remains an important identity control, and Microsoft continues to recommend it along with phishing-resistant authentication methods such as passkeys or hardware security keys. Authentication confirms who the user is. It does not confirm what that user is authorizing, or who ends up holding the access.
In a device code attack, MFA may successfully authenticate the legitimate employee. But if that employee is entering a code tied to an attacker-controlled session, the resulting authorization can still go to the attacker. The FBI’s Kali365 warning describes attackers getting into Microsoft 365 using those stolen sign-in keys, with no further password or MFA prompt required.
That distinction is important for law firms because it reinforces a broader Microsoft 365 security gap many firms do not actively monitor. Proving identity at the front door tells the firm nothing about how that access is used afterward.
A trusted identity gives an attacker more than inbox access
Once an attacker gains valid Microsoft 365 access, the value is not limited to reading email. Microsoft observed attackers mapping organizational relationships and permissions, identifying financial and executive users, creating malicious inbox rules and searching communications for details such as wire instructions and pending invoices. In some observed cases, attackers registered their own devices on the account within 10 minutes, so their access would survive even a password reset.
Inside a law firm, authenticated access can provide something especially useful to an attacker: context. Access to normal communications may reveal who works together, which client matters are active, who approves payments and how attorneys, administrators and clients typically communicate. An attacker can use that context to make a later request far more convincing.
That is one reason account compromise can create the conditions for business email compromise in law firms, where payment or invoice fraud arrives from a real, trusted account rather than a suspicious outside address. The attacker may spend time observing before attempting financial fraud, impersonation or further data access.
For law firms, that can also put confidential client communications and matter information at risk. The specific legal and professional implications will depend on the circumstances and jurisdiction, but detecting unauthorized access quickly can materially affect the scope of an incident and the firm’s response.
Security awareness needs a new question
Device code phishing does not mean attorneys should start distrusting every authentication request. That would make daily work nearly impossible and would probably result in security guidance being ignored altogether. Instead, awareness training needs to account for the fact that a legitimate login page does not validate the workflow that led to it.
One useful question to reinforce is: Was I expecting to authorize this?
Employees should be encouraged to pause when an unexpected document, email or outside party asks them to enter a device code, even if they ultimately land on a familiar authentication page. Unusual authentication instructions can be verified through another trusted channel before access is approved.
Training examples should also reflect how lawyers actually work. A generic fake bank email may check a compliance box, but a convincing DocuSign request or secure-document workflow is far closer to the attacks users may actually encounter.
Identity security needs controls on both sides of authentication
Reducing device code phishing risk requires more than employee vigilance. Law firm IT teams should look at controls before and after authentication.
Reduce unnecessary authorization paths
Microsoft recommends allowing device code authentication only when it is actually needed and blocking the method entirely where possible. The FBI recommends conditional access, the Microsoft 365 rules that control who can sign in and under what conditions, to restrict device code authentication while maintaining limited exceptions for required business processes. Firms should audit legitimate usage before applying broad restrictions.
Tighten identity and application governance
Review which third-party apps are connected to firm accounts and what data each one is allowed to reach, continue using MFA and consider phishing-resistant authentication methods where appropriate. Unexpected applications, permissions or authorization activity should have a clear review path.
Monitor activity after authentication
Even strong preventive controls will not stop every compromise. Monitoring activity after authentication can surface indicators such as abnormal mailbox behavior, suspicious file access, unauthorized applications, unexpected devices or other activity that deviates from the user’s normal behavior.
Trusted access needs ongoing verification
Law firms depend on digital trust. Attorneys need to move between documents, systems, clients and outside parties without turning every authentication event into an IT project. Device code phishing exploits that expectation. It demonstrates why identity security cannot be reduced to a successful login or MFA prompt. Firms need controls that make inappropriate authorization harder and enough visibility to recognize when an account begins behaving in ways the legitimate user would not.
For firms using the Afinety Cloud Platform, Microsoft 365 Identity Defense is included as an additional layer of protection. It monitors activity across Outlook, SharePoint, Teams and OneDrive for indicators of account compromise, with investigation and response handled by Afinety rather than adding another alert queue for the firm’s internal team.
Email security, MFA, conditional access and employee training remain important. The additional question for law firms is whether they can recognize when legitimate access starts being used in ways the employee never intended.